Related Experiment Video
Updated: Oct 10, 2025

Analysis of SEC-SAXS data via EFA deconvolution and Scatter
Published on: January 28, 2021
An anonymous SIP authenticated key agreement protocol based on elliptic curve cryptography
1School of Safety Science and Engineering, Civil Aviation University of China, Tianjin, China.

Abstract:
Designing a secure authentication scheme for session initial protocol (SIP) over internet protocol (VoIP) networks remains challenging. In this paper, we revisit the protocol of Zhang, Tang and Zhu (2015) and reveal that the protocol is vulnerable to key-compromise impersonation attacks. We then propose a SIP authenticated key agreement protocol (AKAP) using elliptic curve cryptography (ECC). We demonstrate the correctness of the protocol using Burrows-Abadi-Needham (BAN), and its security using the AVISPA simulation tool. We also evaluate its performance against those of Zhang, Tang and Zhu, and others.
Related Concept Videos
 01:35
Asymmetric Lipid Bilayer
 02:36
Crown Ethers
 01:24
[3,3] Sigmatropic Rearrangement of Allyl Vinyl Ethers: Claisen Rearrangement
 02:31
Protection of Alcohols
Protection
It defines a protecting group as the masking agent to make the more reactive species inert to a given set of conditions. This concept is depicted via the illustration of liquid flow through different outlets in an assembly of pipes. The analogy helps to understand the role...
 01:25
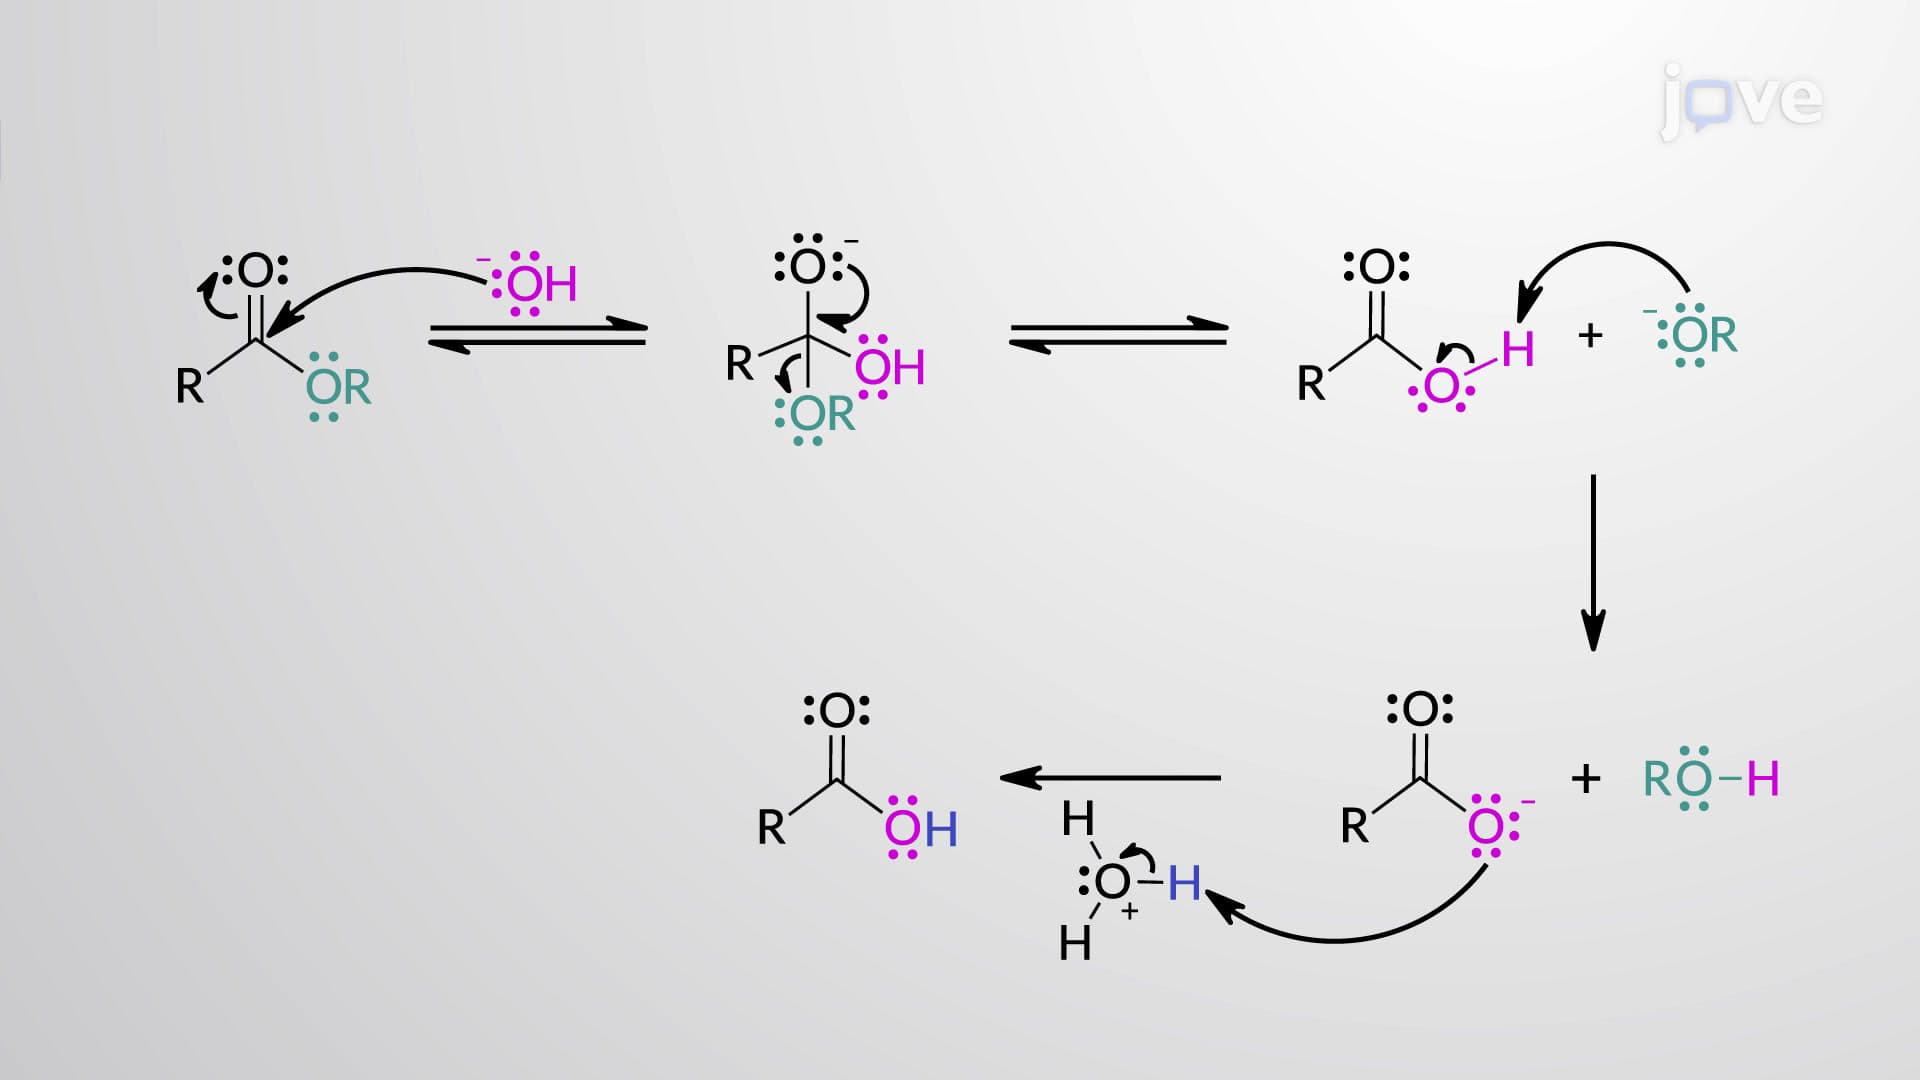
Esters to Carboxylic Acids: Saponification
The reaction requires a base in stoichiometric amounts, which participates in the reaction and is not regenerated later. So, the base acts as a...
 01:26
Inductively Coupled Plasma Atomic Emission Spectroscopy: Instrumentation
There are three main types of inductively coupled plasma atomic emission spectroscopy (ICP-AES) instruments: sequential, simultaneous multichannel, and Fourier transform instruments, with the latter being less commonly used....