Related Experiment Video
Updated: Jul 7, 2025

Integration of 5G Experimentation Infrastructures into a Multi-Site NFV Ecosystem
Published on: February 3, 2021
Provably Secure Lightweight Mutual Authentication and Key Agreement Scheme for Cloud-Based IoT Environments
1Department of Computer Engineering, College of Engineering, Keimyung University, Daegu 42601, Republic of Korea.

Abstract:
A paradigm that combines cloud computing and the Internet of Things (IoT) allows for more impressive services to be provided to users while addressing storage and computational resource issues in the IoT environments. This cloud-based IoT environment has been used in various industries, including public services, for quite some time, and has been researched in academia. However, various security issues can arise during the communication between IoT devices and cloud servers, because communication between devices occurs in open channels. Moreover, issues such as theft of a user's IoT device or extraction of key parameters from the user's device in a remote location can arise. Researchers interested in these issues have proposed lightweight mutual authentication key agreement protocols that are safe and suitable for IoT environments. Recently, a lightweight authentication scheme between IoT devices and cloud servers has been presented. However, we found out their scheme had various security vulnerabilities, vulnerable to insider, impersonation, verification table leakage, and privileged insider attacks, and did not provide users with untraceability. To address these flaws, we propose a provably secure lightweight authentication scheme. The proposed scheme uses the user's biometric information and the cloud server's secret key to prevent the exposure of key parameters. Additionally, it ensures low computational costs for providing users with real-time and fast services using only exclusive OR operations and hash functions in the IoT environments. To analyze the safety of the proposed scheme, we use informal security analysis, Burrows-Abadi-Needham (BAN) logic and a Real-or-Random (RoR) model. The analysis results confirm that our scheme is secure against insider attacks, impersonation attacks, stolen verifier attacks, and so on; furthermore, it provides additional security elements. Simultaneously, it has been verified to possess enhanced communication costs, and total bit size has been shortened to 3776 bits, which is improved by almost 6% compared to Wu et al.'s scheme. Therefore, we demonstrate that the proposed scheme is suitable for cloud-based IoT environments.
Related Concept Videos
 00:52
Social Proof
 01:24
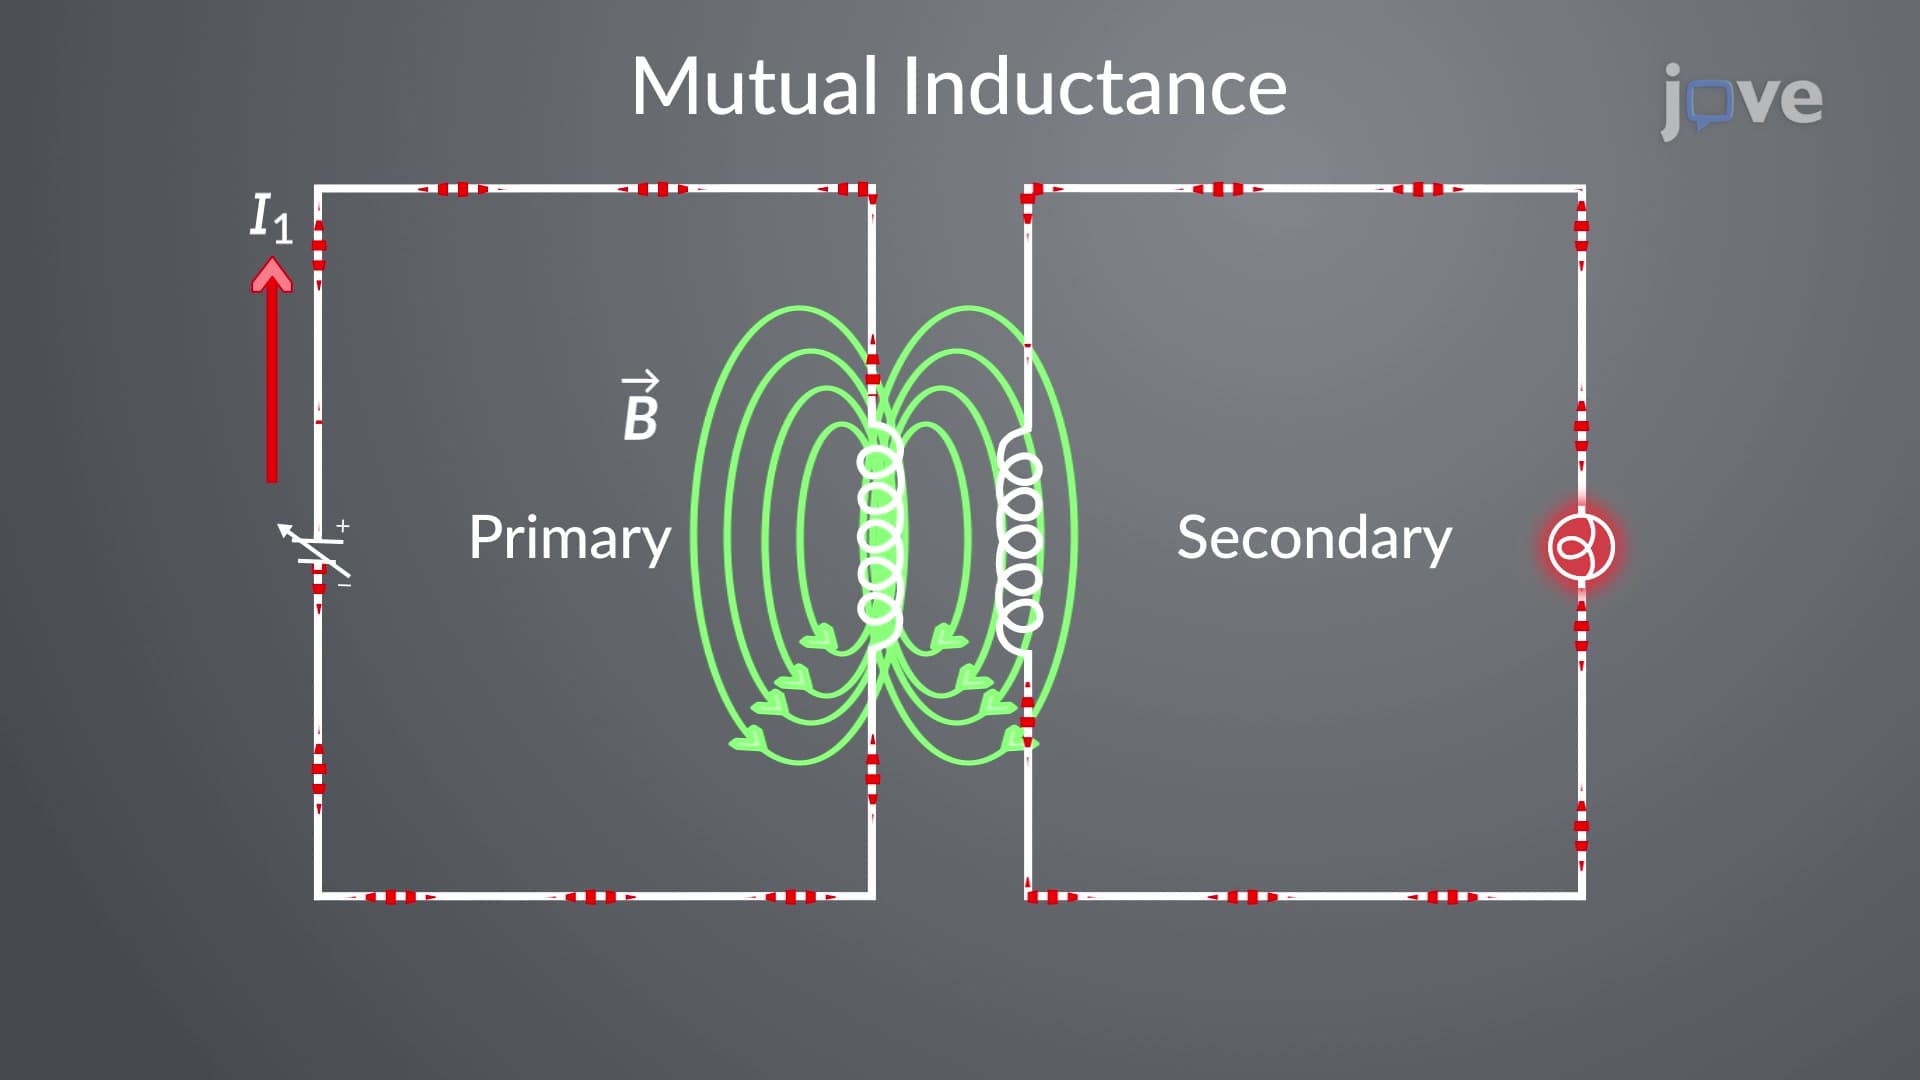
Mutual Inductance
When two circuits carrying time-varying currents are close to one another, the magnetic flux through each circuit varies because of the changing current in the other circuit. Consequently, an emf is induced in each circuit by the changing current in the other. Therefore, this type of emf is called...
 01:35
Asymmetric Lipid Bilayer
 03:21
Weak Base Solutions
 01:18
Principle of Equivalence
 01:25
Distribution Reliability and Automation