Related Experiment Video
Updated: May 11, 2025
Author Spotlight: Innovations in iTUG Test for Enhanced Risk Assessment and Cognitive Insights
Published on: October 25, 2024
AI-driven cybersecurity framework for software development based on the ANN-ISM paradigm
Habib Ullah Khan1, Rafiq Ahmad Khan2, Hathal S Alwageed3
1Department of Accounting and Information Systems, College of Bussiness and Economics, Qatar University, Doha, Qatar. Habib.khan@qu.edu.qa.

Abstract:
With the increasing reliance on software applications, cybersecurity threats have become a critical concern for developers and organizations. The answer to this vulnerability is AI systems, which help us adapt a little better, as traditional measures in security have failed to respond to the upcoming threats. This paper presents an innovative cybersecurity framework using AI, by the Artificial Neural Network (ANN)-Interpretive Structural Modeling (ISM) model, to improve threat detection, vulnerability assessment, and risk response during software development. This framework helps realize dynamic, intelligent security as a part of the Software Development life cycle (SDLC). Initially, existing cybersecurity risks in software coding are systematically evaluated to identify potential gaps and integrate best practices into the proposed model. In the second phase, an empirical survey was conducted to identify and validate the findings of the systematic literature review (SLR). In the third phase, a hybrid approach is employed, integrating ANN for real-time threat detection and risk assessment. It utilizes ISM to analyze the relationships between cybersecurity risks and vulnerabilities, creating a structured framework for understanding interdependencies. A case study was conducted in the last stage to test and evaluate the AI-driven cybersecurity Mitigation Model for Secure Software Coding. A multi-level categorization system is also used to assess maturity across five key levels: Ad hoc, Planned, Standardized, Metrics-Driven, and Continuous Improvements. This study identifies 15 cybersecurity risks and vulnerabilities in software coding, along with 158 AI-driven best practices for mitigating these risks. It also identifies critical areas of insecure coding practices and develops a scalable model to address cybersecurity risks across different maturity levels. The results show that AI outperforms traditional systems in detecting security weaknesses and simultaneously fixing problems. During Levels 1-3 of the system improvement process, advanced security methods are used to protect against threats. Our analysis reveals that organizations at Levels 4 and 5 still need to entirely shift to using AI-based protection tools and techniques. The proposed system provides developers and managers with valuable insights, enabling them to select security enhancements tailored to their organization's development stages. It supports automated threat analysis, helping organizations stay vigilant against potential cybersecurity threats. The study introduces a novel ANN-ISM framework integrating AI tools with cybersecurity modeling formalisms. By merging AI systems with secure software coding principles, this research enhances the connection between AI-generated insights and real-world cybersecurity usage.
More Related Videos
 07:49
Automated Deployment of an Internet Protocol Telephony Service on Unmanned Aerial Vehicles Using Network Functions Virtualization
Published on: November 26, 2019
 05:21
Characterization of the Sense of Agency over the Actions of Neural-machine Interface-operated Prostheses
Published on: January 7, 2019
Related Concept Videos
 01:19
High-Level and Low-Level Awareness
 01:19
Quality Assurance
 02:16
Stereotype Content Model
 02:53
Adaptive Mechanisms in Cancer Cells
Some of the advantages that cancer cells have on normal cells include - enhanced ability to divide without terminally differentiating, induce new blood vessel formation,...
 01:19
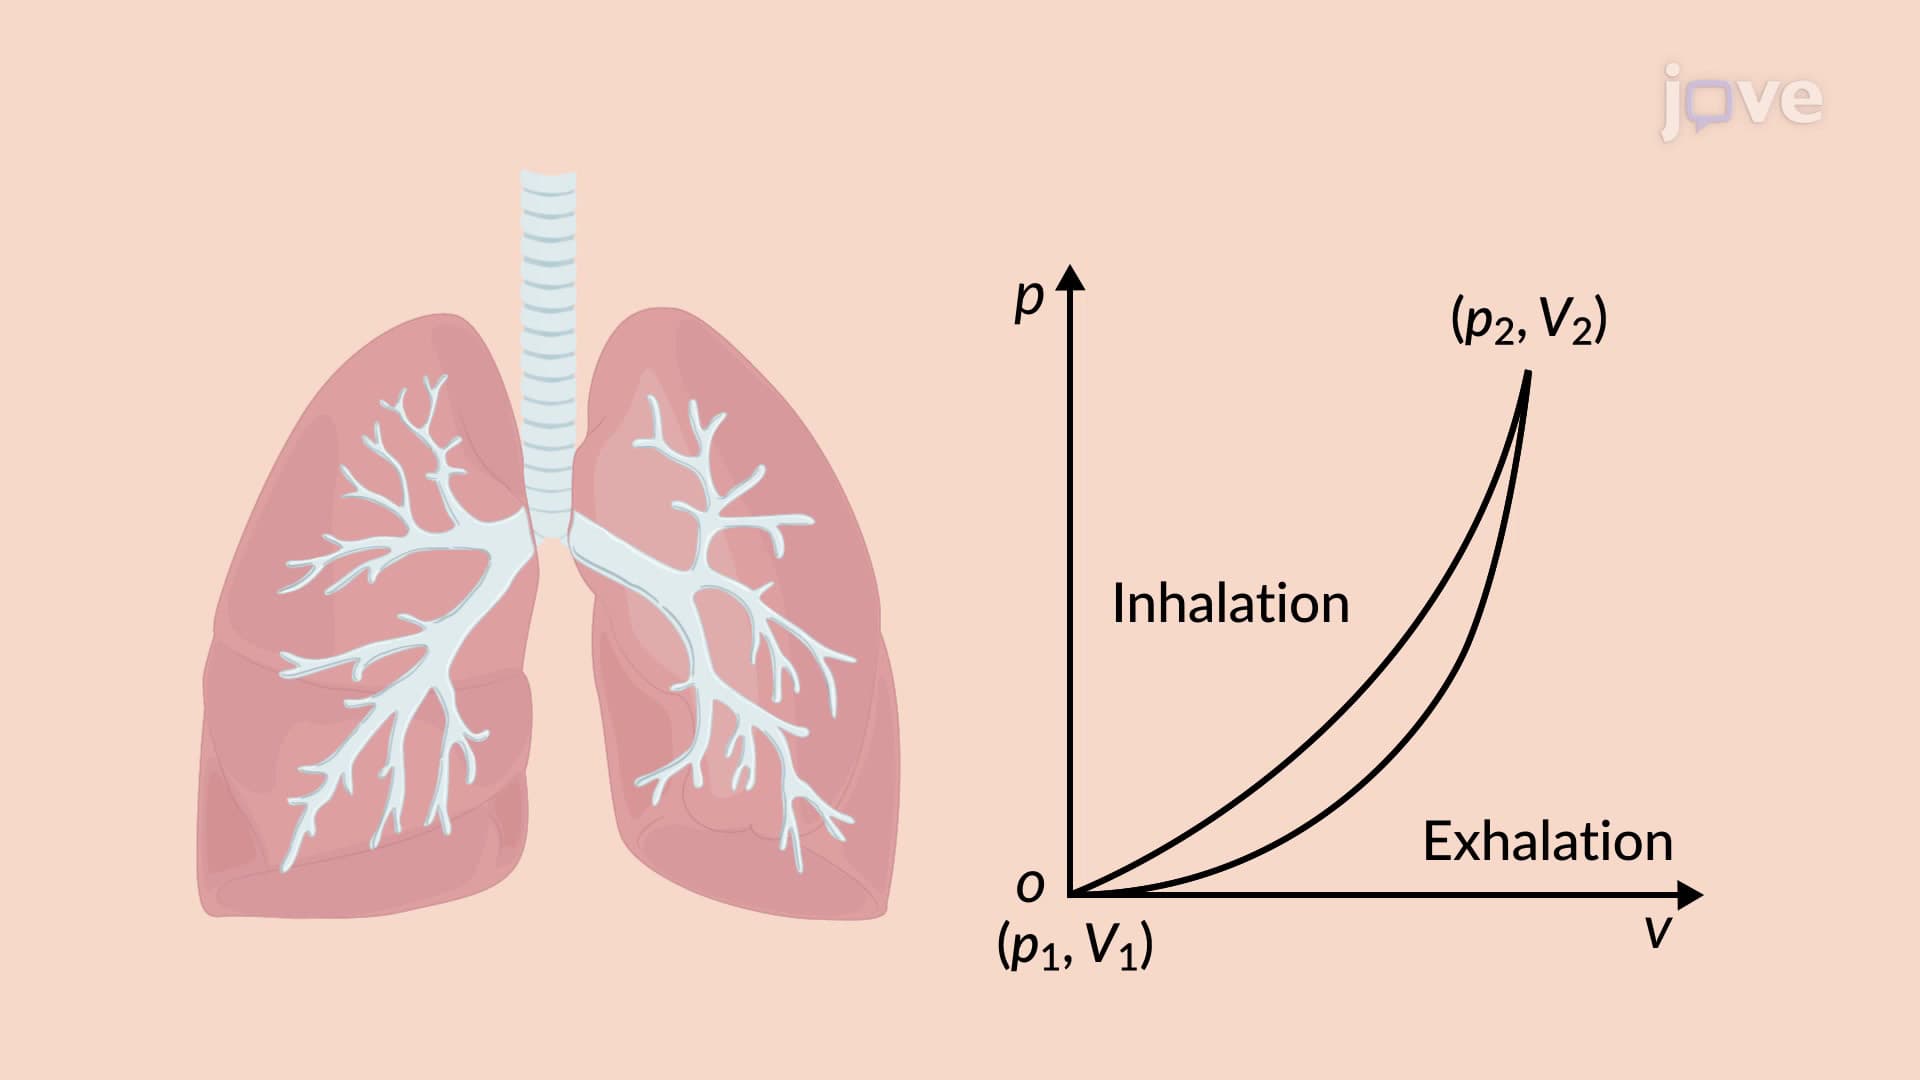
Cyclic Processes And Isolated Systems
In the case of a non-isolated system, the change in the internal energy is zero only if the process is cyclic. A thermodynamic process is considered cyclic if the system undergoes a series of changes and returns to its initial state.
Consider a cyclic process that returns to its initial state, undergoing a four-step process. The heat transfer along each...
 01:27
Nursing Clinical Information System
A Nursing Clinical Information System (NCIS) is a specialized type of healthcare information system tailored to meet the unique needs of nursing practice. It incorporates the principles of nursing informatics to streamline information management and improve the quality of care delivery.
Critical attributes of NCIS include: