Related Experiment Video
Updated: May 3, 2026
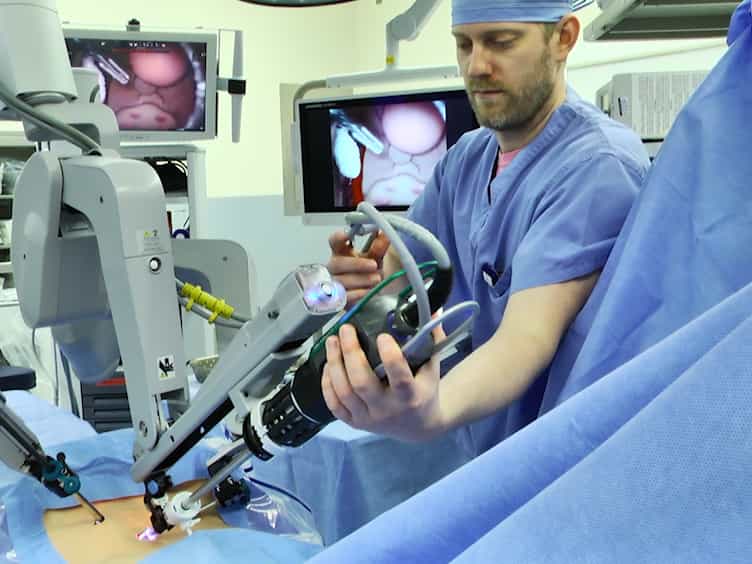

Emergency Undocking in Robotic Surgery: A Simulation Curriculum
Published on: May 20, 2018
Tactical security controls for unpredictable events: Aligning security tactics with business continuity for
Rachelle Loyear1, M G William J Walker2
1Vice President of Integrated Security Solutions, Allied Universal.

Abstract:
Unpredictable threats, ranging from civil unrest and cyber-physical disruptions to infrastructure failures, continue to challenge security and business continuity professionals. Traditional risk management approaches often fail in these fast-evolving scenarios, necessitating a shift toward tactical security controls that are adaptable, scalable and integrated within business continuity frameworks. This paper explores the security effects model, a strategic approach that categorises security controls based on the outcomes they achieve rather than the specific threats they address. By leveraging seven key security effects - deterrence, access control, detection, assessment, delay, response, and recording and communication - organisations can design security postures that remain effective even in highly dynamic environments. Among the abovementioned seven, the paper identifies four mission-critical security effects for unpredictable threats: detection, assessment, delay and response. By aligning security controls with these mission-critical effects, organisations can enhance early warning capabilities, streamline crisis assessment, buy critical response time and ensure cohesive multiteam coordination. Using a structured 'what if?' methodology, the paper demonstrates how organisations can proactively identify vulnerabilities and prepare security measures that are functional across multiple threat vectors. A case example using the Francis Scott Key Bridge collapse illustrates how applying this approach can improve security resilience against both accidental and intentional disruptions. The paper provides practical, actionable guidance for security and business continuity professionals, emphasising the need for an integrated security-continuity framework that aligns with industry best practices, including ISO 22301 and American Society for Industrial Security (ASIS) enterprise security risk management (ESRM). By shifting away from reactive security models to proactive, effects-based tactical controls, organisations can build resilience against the unknown while ensuring operational continuity in the face of emerging threats. This article is also included in The Business & Management Collection which can be accessed at https://hstalks.com/business/.
Related Concept Videos
 01:22
Design Consideration
The factor of safety is another key...
 01:10
Control Systems
At the heart...
 01:23
Types of Biopharmaceutical Studies: Controlled and Non-Controlled Approaches
Non-controlled studies, commonly employed for initial exploration, lack a control group, rendering them susceptible to biases and external influences. In contrast,...
 01:18
Steps in Outbreak Investigation
 01:15
Assumptions of Survival Analysis
 01:27
Coping Strategies: Problem Focused
For example, consider a student who struggles to understand their...