Related Experiment Videos
Q-LEASE: Lifecycle-bound zero-trust authorization for HPC-to-QPU job handoffs
Fouad Ailabouni1,2,3, Jesús-Ángel Román-Gallego1,2,4
1Departamento de Informática y Automática, Escuela Politécnica Superior de Zamora, Universidad de Salamanca, Zamora, 49029, Spain.

Background:
Zero-Trust access control for cloud APIs is well established, but hybrid High-Performance Computing (HPC)-to-Quantum Processing Unit (QPU) workflows have a lifecycle existing mechanisms were not built for: a job queues for minutes to days, is dispatched, executes, and only then releases results, while identity, policy, and hardware calibration state can change throughout. Existing token, proof-of-possession, and workload-identity mechanisms do not separate permission to queue from permission to execute, nor bind authorization to current hardware state.
Methods:
We designed and implemented Q-LEASE, a two-capability protocol separating a Queue Admission Ticket from a single-use Execution Capability bound to a circuit hash, backend identity, and calibration epoch, re-evaluated by a real Open Policy Agent (OPA) engine immediately before dispatch. The prototype uses real Ed25519/PASETO tokens, DPoP-style proof-of-possession, SPIFFE-shaped workload identity, and a phase-aware revocation state machine, deployed as six containerised services on a Kubernetes ( kind) cluster with Kueue-driven queueing. We compared Q-LEASE against four representative baselines across 16 attack/failure scenarios (2400 attack trials, 500 clean trials), and verified core safety properties with TLA+/TLC and token-flow security with the Tamarin prover.
Results:
Q-LEASE blocked 90.0% of unauthorized-execution attempts (95% confidence interval (CI) 87.0-92.4%), versus 12.5-37.9% for the four baselines. The remaining gap came from queue/execution separation and circuit/backend/calibration-epoch binding, which no baseline implements. Both TLA+ safety properties held, and all five Tamarin lemmas were proved automatically. Q-LEASE's mean policy-decision latency was 44.3 ms, approximately 34.4 ms higher than the baselines, with no measurable increase in end-to-end workflow completion time relative to a real, contention-driven queue wait, while running against a real Kueue-admitted workload on a real cluster.
Conclusions:
Separating queue admission from execution authorization, and binding it to hardware state re-checked immediately before dispatch, closes a gap that composing existing OAuth-family mechanisms does not, at a latency cost small relative to realistic QPU queue waits.
Related Concept Videos
 02:28
Leaky Scanning
 01:25
Types of Reports I: Hand-off Report
Following are the key components and categories of hand-off reports:
Purpose and Process:
 01:11
IP3/DAG Signaling Pathway
 02:33
Hedgehog Signaling Pathway
 01:19
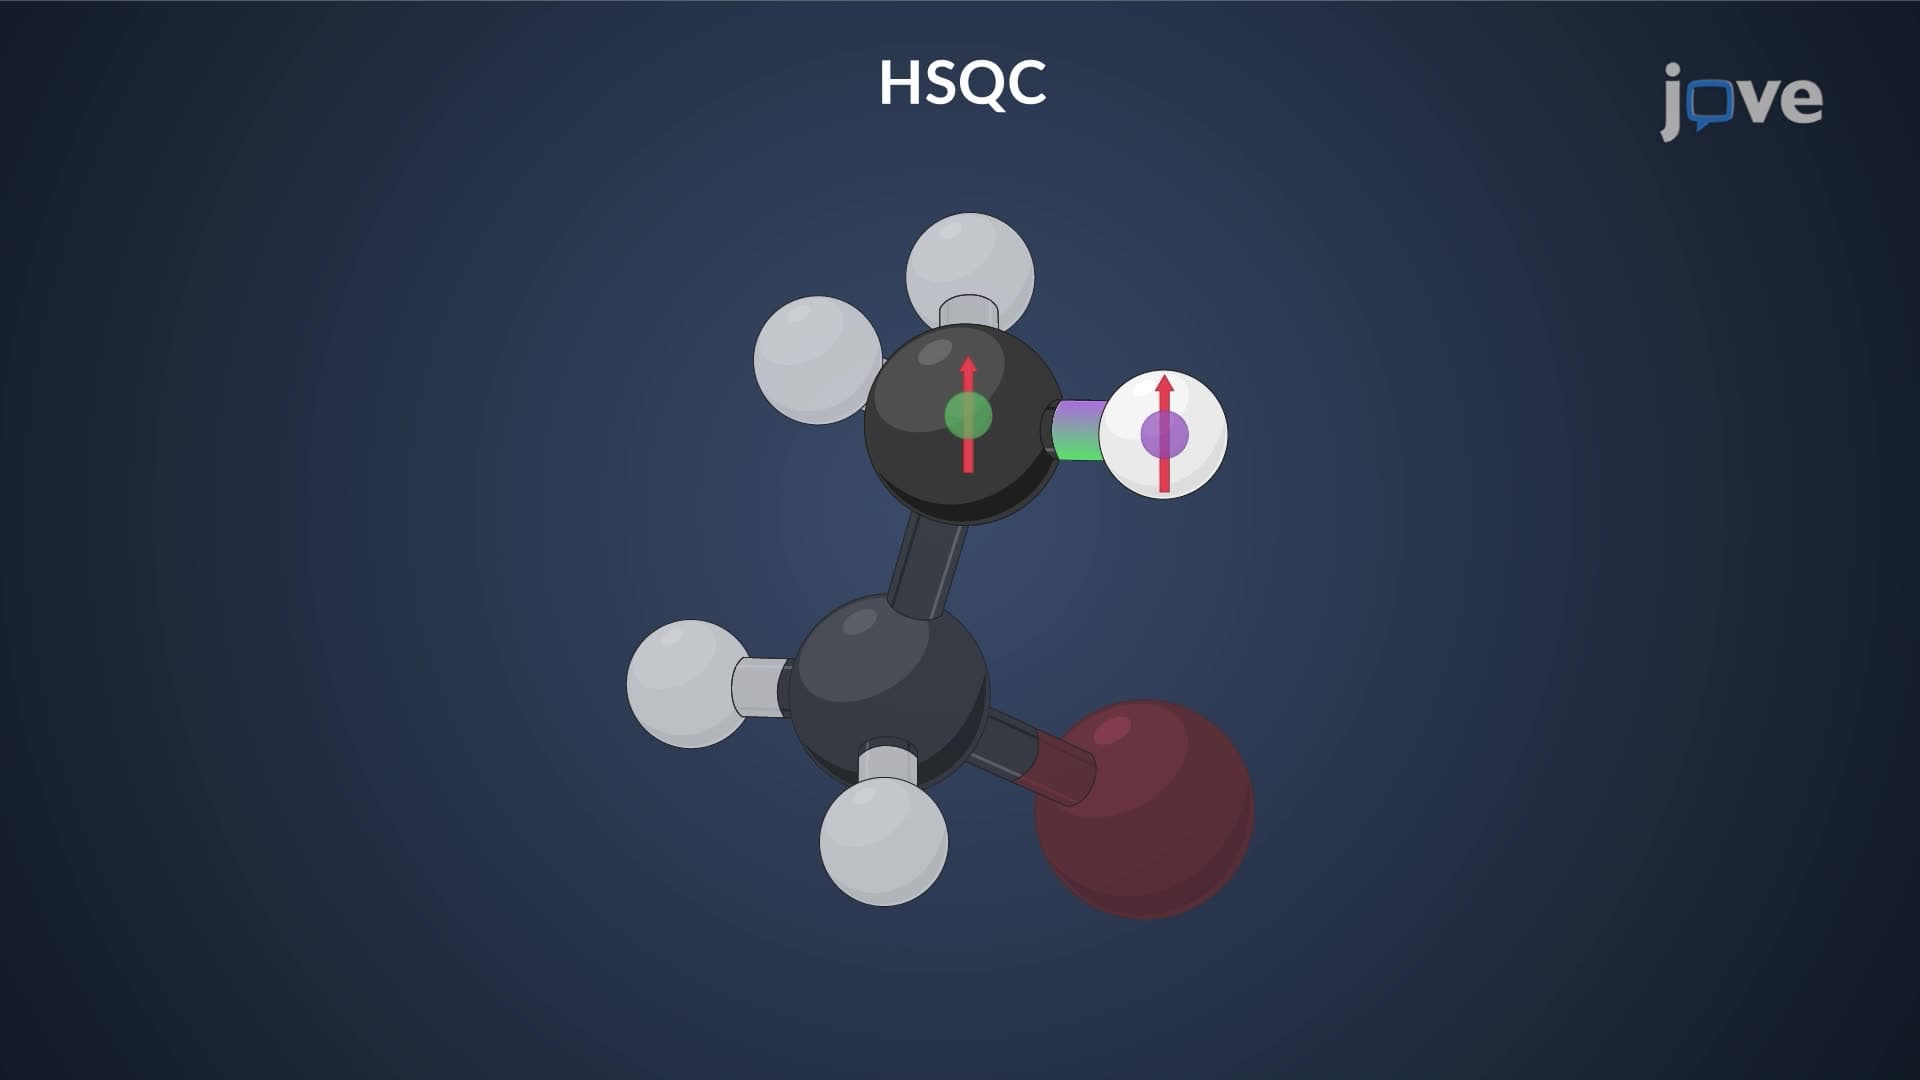
2D NMR: Heteronuclear Single-Quantum Correlation Spectroscopy (HSQC)
 01:27
¹H NMR: Long-Range Coupling
In alkenes, spin information is communicated via σ–π overlap, as seen in allylic (four-bond) and homoallylic (five-bond) couplings. These coupling interactions are stronger when the σ bond is parallel to the alkene π orbitals.